


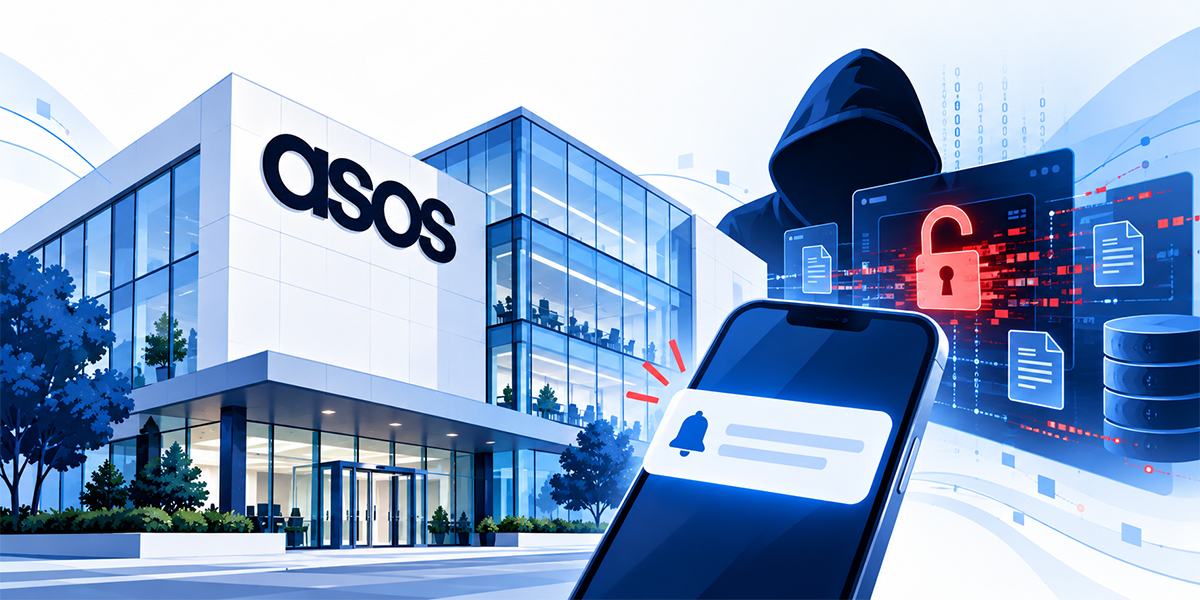
If you were looking at your phone on October 6, 2026, and happened to have the ASOS app installed, you probably saw a message pop up that no corporate legal team ever wants to explain to a board.
It wasn’t an autumn sale or a shipping update. It was a push alert that said, plain as day: ASOS HACKED.
The notification claimed that a hacker group called Xuanye Group had broken into an internal Snowflake data system, leaving a direct ransom note for ASOS’s Data Protection Officer and IT team.
ASOS moved fast to cut off access to the notification tool, issued a statement telling customers to ignore the alert, and called in external incident response teams. They later mentioned that basic details—like customer names and emails—might have been exposed, though payment info and passwords appeared safe. Still, the news hit hard enough that ASOS stock dropped about 10% almost immediately.
Now, ASOS is based in the UK, but if you work with any business that connects customer information to third-party apps, don’t write this off as someone else’s problem. The exact same scenario could easily happen to almost any company today.
The Actual Threat Vector Wasn't What People Thought
Most data breach headlines follow a predictable script: bad actor finds a hole in a central database, pulls millions of records, leaves.
This one was different, and frankly, more annoying from a risk perspective. The attackers didn’t necessarily need to shatter Snowflake’s core platform—Snowflake quickly pointed out that its central infrastructure was completely fine.
Instead, someone likely got hold of credentials or an unauthenticated token connected to a third-party messaging platform that ASOS used to send app alerts.
And that’s the trap for legal departments.
We audit customer databases. We spend months negotiating data processing agreements for core cloud storage. But marketing tools? Push notification engines? Third-party API integrations?
They usually live with product or growth teams, far away from legal or CISO oversight. Nobody treats a push notification vendor like a high-risk security endpoint—until that vendor broadcasts an unauthorized ransom note to your entire user base in five seconds flat.
If an attacker gets write access to your communication channels, what else can they reach through those same integrated pipelines? That’s the question General Counsels should be asking their IT leaders today.
The Legal Pile-Up Happens All At Once
When an alert like this goes out, the legal workload doesn’t trickle in—it dumps on your desk within an hour.
First, you’re dealing with a chaotic patchwork of breach notification laws. In the US, every state defines personal information slightly differently. Does a name tied to a phone number trigger a reporting requirement in California? What about Texas or New York? You’re forced to make threshold calls while the forensic team is still figuring out what was actually touched.
If you’re a public company, the SEC’s four-day Form 8-K disclosure clock starts ticking the moment an incident is deemed material. Deciding when something becomes material under active extortion is a legal high-wire act.
Then come the class action firms. Plaintiffs’ lawyers don’t wait for a final forensic audit; they file based on news reports. If your company’s name is trending alongside “breach,” complaints can land in federal court before your incident commander has even finished their second cup of coffee.
And don’t forget privilege. Courts have become increasingly hostile toward claims that forensic breach reports are protected under attorney-client privilege.
If your IT department retains the forensic firm directly under a standard commercial contract, you’ll likely end up handing that report over in discovery. Legal counsel has to structure that engagement from minute one.
Where Teams Actually Fail: The Paper Trail
The hardest part of a breach like this isn’t always the high-level decision-making. It’s the sheer volume of administrative and legal work that follows.
Within 48 hours of an incident, you’re looking at thousands of system logs, vendor contracts, internal Slack channels, customer inquiries, and regulatory correspondence. Someone has to review it all, redact sensitive information, flag privilege, and compile a clear timeline that partners or executives can actually use.
Senior in-house lawyers shouldn’t be spending 3:00 AM coding documents or cross-referencing vendor liability caps. That wastes expensive talent and invites burnout.
The smart move—and what well-run legal departments do—is splitting the workflow early. Let your core team focus on strategic calls and regulatory discussions, and hand off the heavy, process-driven document review to a dedicated support team that can scale up immediately.
What To Clean Up Before The Next Headline
If you want to protect your team before an alert like this hits your company’s app, a few preventative steps go a long way:
- Find the hidden integrations. Ask IT for a complete list of every third-party marketing, push, and messaging tool that touches user data or talks to your app.
- Enforce MFA everywhere. No exceptions for marketing accounts or legacy APIs. Stolen credentials are still the easiest way in.
- Fix your forensic retainer process. Make sure any external incident response firm is retained directly by outside or in-house legal counsel under explicit privilege protocols.
- Line up litigation support early. Know who you'll call when you suddenly need to process 50,000 vendor agreements or log files on a 72-hour deadline.
A Quick Word On Handling The Workload
When a cyber incident or high-volume litigation hits, internal legal teams get stretched thin almost immediately. That’s where Aeren LPO comes in.
Instead of burning out your team on late-night document reviews, contract audits, or eDiscovery processing, Aeren LPO provides experienced, on-demand legal support teams to handle the heavy lifting.
We help corporate counsel and law firms manage massive document volumes quickly, accurately, and cost-effectively so you can keep your focus where it belongs—on strategy.
Legal Disclaimer: The information provided in this article is for educational and informational purposes only and does not constitute formal legal or technical advice. Organizations should consult qualified legal counsel and cybersecurity professionals regarding specific incident response protocols and regulatory compliance obligations.
Explore Cyber Incident Response Review
Strengthen your organization’s preparedness with our tailored review.